I find the way in before anyone else does.
Penetration tester, 3+ years. Web apps, networks, cloud and mobile, tested by hand and written up so your team can fix it.
Email AndrewWhat I test
Web apps and APIs
Auth, access control and business logic.
Internal networks and AD
One foothold to domain admin.
External and cloud
Your internet edge, IAM and storage.
Mobile
Android, iOS and the APIs behind them.
OSINT
What the internet already says about you.
How a test runs
Scope
Targets, dates and rules of engagement, agreed in writing.
Recon
Map what is exposed before touching any of it.
Exploit
Every finding reproduced by hand before it is reported.
Report
Plain risk, steps to reproduce and a fix for each finding.
Hiring for a security role?
Email me the roleVelocity
My open-source OSINT console: live aircraft, ships and satellites on one map.
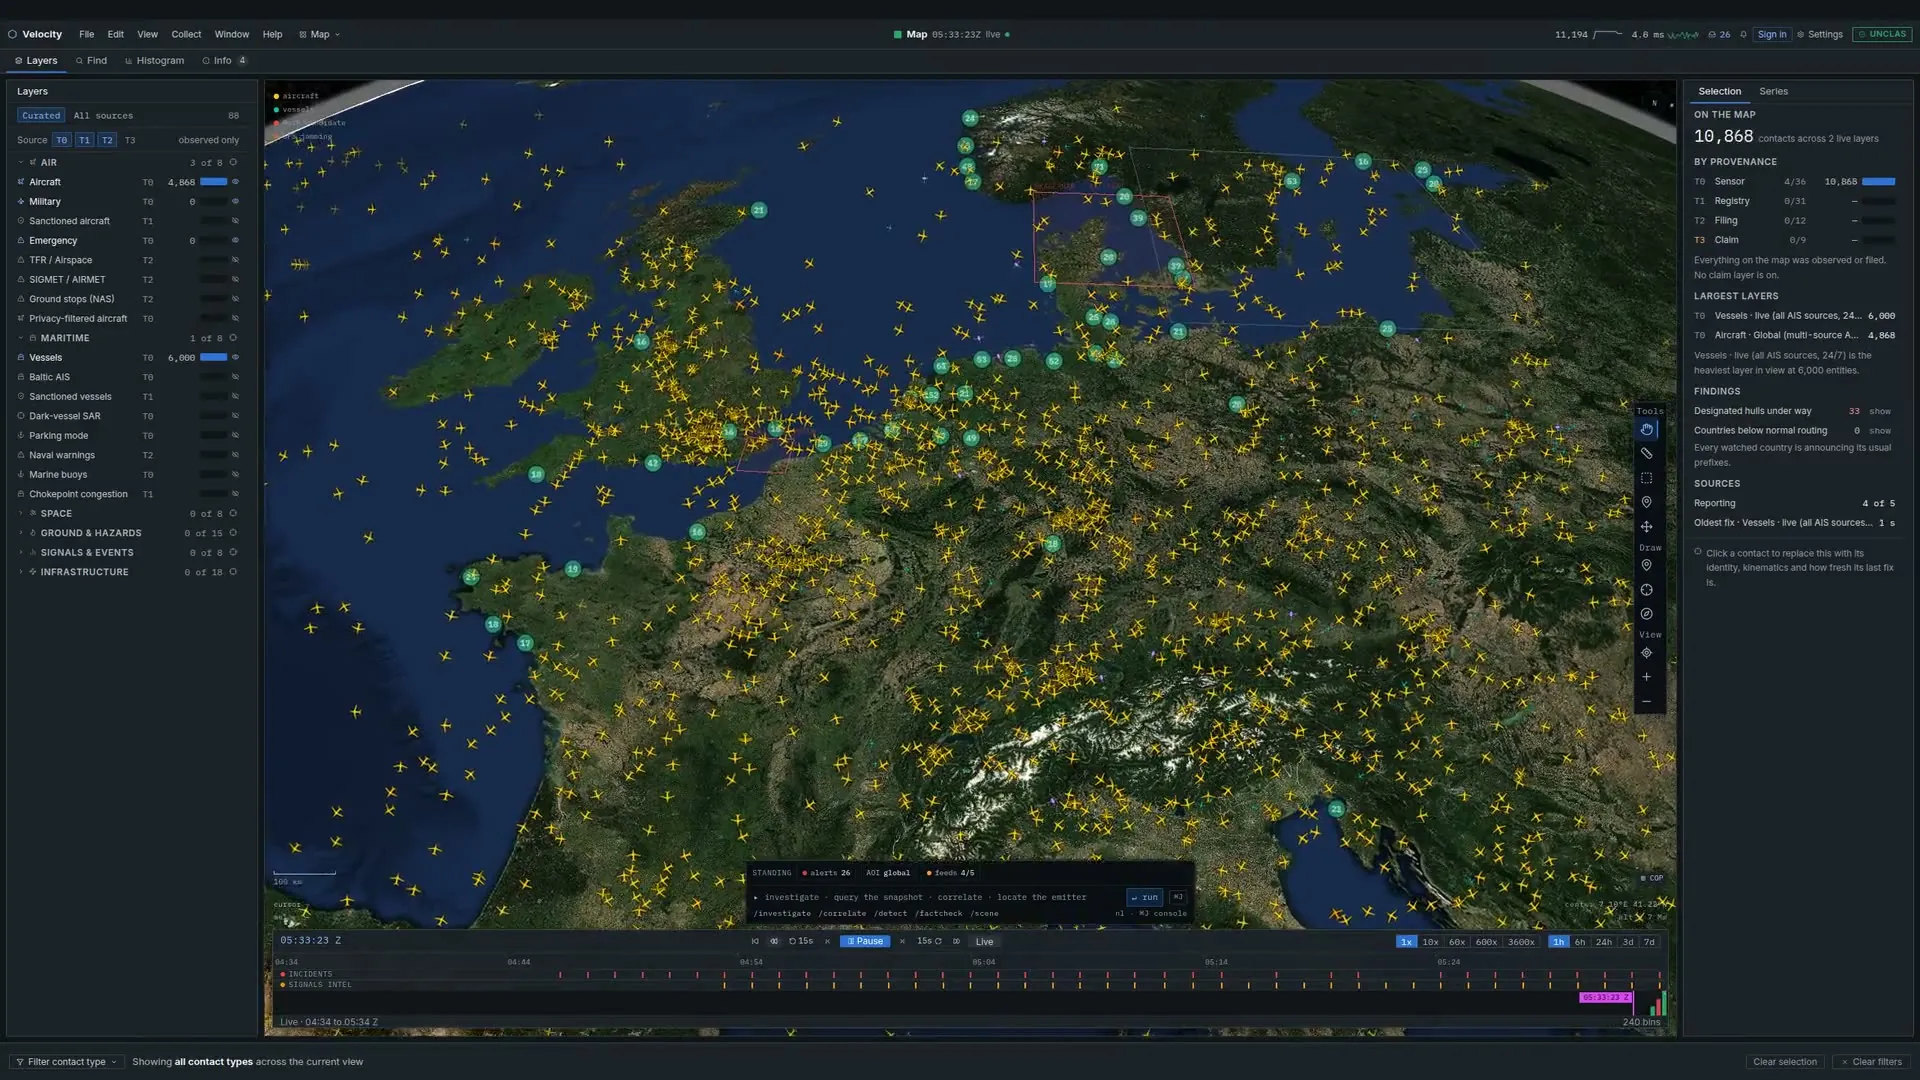
The replay bar: scrub back to any moment in an archive on your own disk.
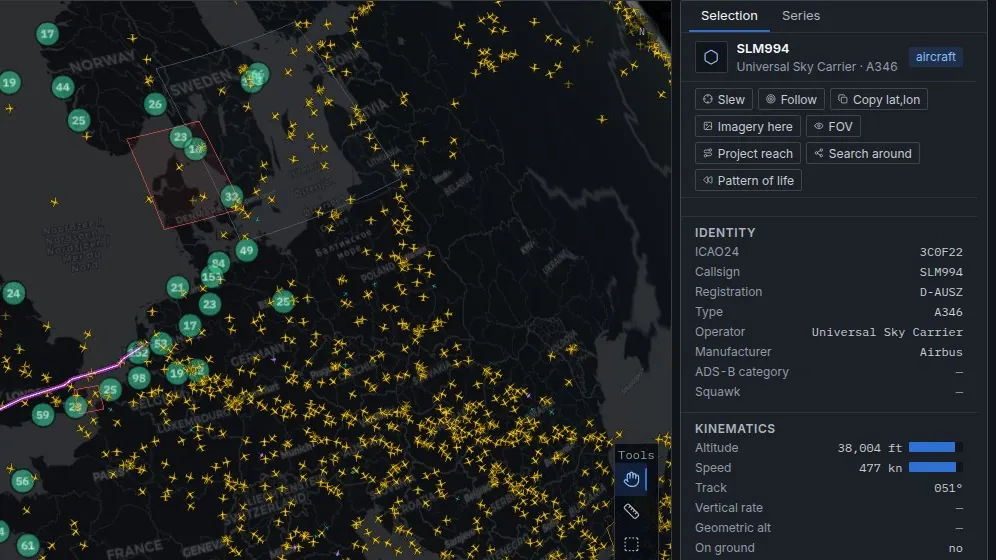
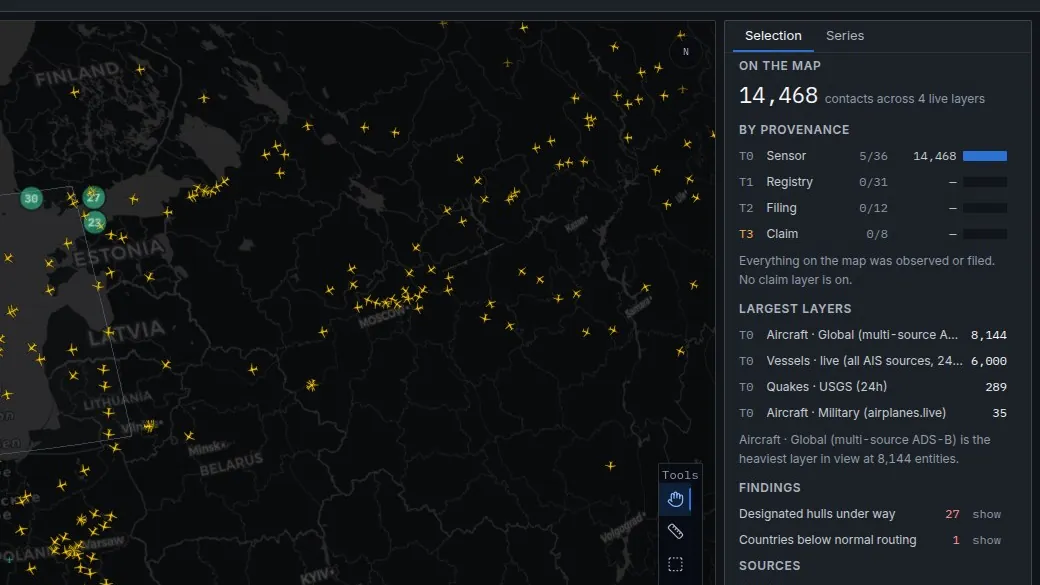
Velocity is public on GitHub, with every test and the self-audit.
Read the case study Watch the repositoryNeed something tested?
Email me the scopeCommon questions
Can you name past clients?
No. Engagements run under NDA, so client names and their findings stay private. What I can show is my method, my scope and the code I publish, including an audit of my own.
Are you open to a full-time role?
Yes. Email me the role, the team and what they test, and I’ll reply.
How do we start a test?
Email the scope, the dates and who I should talk to. I’ll come back with questions before anything is agreed.
What does the report look like?
Each finding gets its risk in plain words, the steps to reproduce it and the fix. The summary at the top is written for whoever signs off the budget.
Can I read your code?
Yes. Velocity is public under AGPL‑3.0 at github.com/AndrewCTF/velocity, with its tests and its security self-audit.